Monday, September 21, 2026
Emerging Companies of the Year 2026
Business Honor
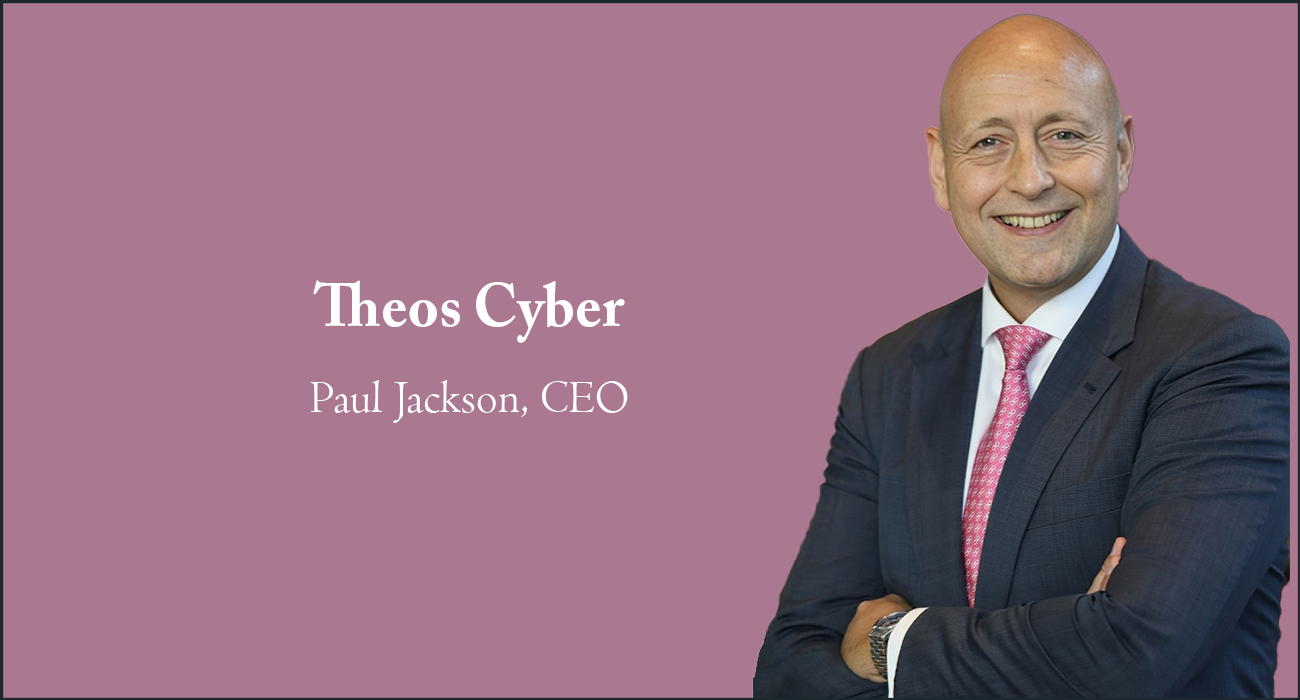 Theos Cyber is a cybersecurity services organization that is committed to providing services aimed at helping organizations bolster their cyber resilience in the wake of an increasingly complex cyber threat environment. Theos Cyber operates in Singapore, Hong Kong, Malaysia, and the Philippines and provides organizations operating in regulated environments in these regions with integrated cybersecurity solutions that cover managed threat detection and response, offensive security, and incident response. Theos Cyber operates under the practitioner-led approach, whereby it utilizes cybersecurity practitioners with experience in the fields of law enforcement, finance, and enterprise security operations. Theos Cyber has incorporated the concept of integrity, accountability, and collaboration in its operations to ensure that cybersecurity is achieved on behalf of its clients. Contrary to most service providers, Theos Cyber does not regard cybersecurity as a single investment but rather focuses on offering continuous protection through intelligence-driven services customized for the needs of every customer.
Services Offered by Theos Cyber
Cyber Defence Service:-
Compromise Assessment
Theos Cyber offers a Compromise Assessment service that enables organisations to verify whether their environments are already compromised by attackers who might have bypassed their current security controls. Specifically designed to help detect threats posed within the Asia-Pacific region, the service utilises advanced threat intelligence, dedicated forensic tools, and expert investigations to identify hidden compromises, methods of persistence, and signs of malicious activities.
Unlike traditional threat detection solutions, the assessment performed by Theos covers endpoints, identity infrastructure, cloud environment, network traffic, and security logs to detect the threats that may have gone unnoticed by automated security systems. Threat intelligence specific to the client’s industry is used at the initial stage to ensure that investigators can concentrate on the most likely attack scenarios.
Professional experts in digital forensics and incident response analyze gathered evidence, perform validation, and build attack timelines if required. After completing the assessment, Theos provides the client with a detailed report highlighting confirmed indicators of compromise, attack sequences, and recommended actions to take. In case any active threats are found, Theos moves into incident response mode.
Managed Threat Detection & Response
Theos Cyber’s MDR service ensures continuous monitoring, threat detection, investigation, and quick response to any threats for organizations through the use of top security platforms like CrowdStrike and Microsoft. Through its advanced detection technologies and practitioner-led approach, it ensures identification, analysis, and containment of cyber threats before any negative impacts on business operations occur.
In contrast to other monitoring services, the service constantly calibratesthe security solutions to fit the threat landscape of the organization. As an extension to the existing security teams, the service offers 24/7 monitoring of endpoints, identities, cloud, and critical infrastructure. Security experts investigate and validate any suspicious activity and conduct a quick response.
Besides, the service offers threat hunting and continuous platform optimization, as well as reports. With the combination of the latest technology, local threat intelligence, and cybersecurity experts, Theos provides organizations in the Asia-Pacific region with improved security, minimized response time, and continuous protection against an increasing number of cyber threats.
Cyber Offense Services
Theos Cyber offers Cyber Offense services to enable organizations to discover and mitigate the potential security vulnerabilities that may be exploited by attackers at any point in time. Provided by skilled cybersecurity professionals, the service uses offensive security techniques and threat intelligence in order to assess the resiliency of enterprise environments. This includes the provision of Vulnerability Assessment and Penetration Testing (VAPT), Red Teaming, Purple Teaming, Vulnerability Management, and Phishing Exercises, offering organizations a holistic view of their security state.
Theos performs CREST-certified penetration testing in networks, web applications, cloud environments, APIs, and mobile platforms and engages in Red Teams for simulating intelligent cyber attacks in assessing detection and response capabilities. Purple Team exercises allow for collaborative engagement of offensive and defensive teams in order to identify and close down security gaps during the process of assessment. Moreover, ongoing vulnerability management focuses on remediation prioritization based on real-world business risk and phishing exercises assess employee awareness through attack simulation scenarios.
Paul Jackson – Short Bio
Paul Jackson is the Chief Executive Officer of Theos Cyber, bringing extensive expertise in digital forensics, cyber investigations, and incident response across the Asia-Pacific region. His career spans leadership roles in both the public and private sectors, including global financial institutions and law enforcement agencies. Paul has also contributed to the advancement of international cybersecurity standards through his work with Interpol and the International Organisation on Computer Evidence (IOCE). In addition to leading Theos Cyber, he hosts Theos Cybernova, the firm's cybersecurity podcast, where he shares insights on emerging cyber threats, security trends, and industry best practices.




.webp)
.webp)

